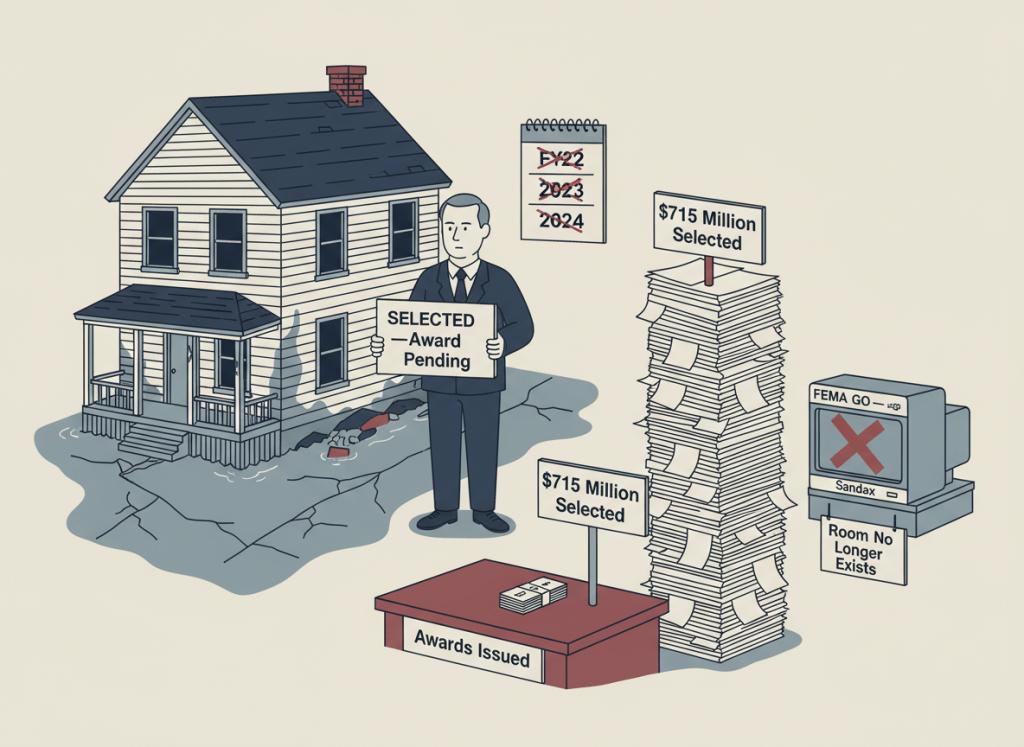
A Perfectly Good Process, Briefly
In fiscal year 2022, the Federal Emergency Management Agency did what a grant agency is supposed to do. According to a new audit from the DHS Inspector General, FEMA received 270 Flood Mitigation Assistance applications seeking $980 million in federal share, awarded $711 million to 230 of them, and endured an auditor’s sample of 30 files without a single deficiency turning up. The notice was posted, the applicants were eligible, and the paperwork existed. Note it carefully, because it is the last time this story is boring.
The money is not abstract. The Infrastructure Investment and Jobs Act handed the program $3.5 billion for fiscal years 2022 through 2026, at $700 million a year, to elevate, buy out, and otherwise rescue flood-insured buildings that keep flooding. Across FY22 and FY23, FEMA awarded $713.5 million. Readers with a calculator will notice that $711 million of that belongs to FY22, which leaves FY23 responsible for roughly $2.5 million. That is not a rounding error. It is the entire year.
Selected Is Not the Same as Paid
The FY23 cycle drew a record 424 subapplications requesting more than $2.35 billion against $800 million available, according to FEMA’s own status page. The OIG counts 197 selected applications worth nearly $715 million. As of August 2025, FEMA had awarded four of them, about $2.5 million, which is under 1 percent of the available money. FEMA’s explanation to the auditors was extended hurricane deployments and Executive Order 14154, Unleashing American Energy, which paused disbursement of IIJA funds.
Both explanations are plausible, and neither is obviously complete. Here is an inference, labeled as one. FEMA’s FY23 status page carries a date of September 23, 2024, and the executive order arrived on January 20, 2025, according to the OIG’s own footnote. If selections were in hand by that September, nearly four months of selected but unpaid money preceded the order. That reasoning rests on two dates and not on any record of when FEMA processed individual awards, so treat it as a question for FEMA and not a finding.
The FY24 cycle fared worse. FEMA published its notice of funding on January 6, 2025 and pulled it on February 13, 2025 for review and revision. The OIG says FEMA planned to reissue it in alignment with the executive order, and found no activity as of July 2025. The same audit helpfully notes that FEMA has up to five years from submission to make awards, after which an application is deemed denied and the money returns to the pool. It is a five-year layaway plan, with the floods supplied by nature.
The Snapshot That Missed the Movie
The report is dated September 28, 2026. Its grant data stops in mid-2025. The auditors carried the cybersecurity story forward through an August 2026 exchange with FEMA, but the grant story froze thirteen months earlier, which matters because FEMA has been busy since.
On April 22, 2026, FEMA announced more than $250 million for over 100 projects under Flood Mitigation Assistance and Swift Current. A regional release described $19.9 million for Alabama, Florida, Kentucky and two other states as working through a backlog, and noted it came 67 days into what FEMA called the longest lapse in appropriations ever. Neither release says which grant cycles the awards belong to. On April 30, the FY24 notice was republished with up to $600 million and an August 6, 2026 application deadline, revised to meet administration priorities. That is about fourteen and a half months between pulled and returned.
Then on July 14, FEMA announced a $600 million FY26 opportunity under Swift Current, open only to states and tribes with a flood-related disaster declaration between June 1, 2025 and May 31, 2027, and project scoping was dropped as an eligible activity. A second inference, also labeled. Those eligibility terms, plus FEMA’s own description of Swift Current as money made available after declared flood disasters, suggest the FY26 cycle reaches communities only after the water has already arrived. A program built to prevent repetitive flood damage is starting to resemble one that responds to it. Whether that is policy or coincidence is another question for FEMA.
The sister program fared no better. GAO reported on September 24, four days before the OIG, that more than $2 billion in BRIC subgrants were still awaiting award as of March 2026, that review took a median of 7 to 9 months, and that FEMA awarded nothing between April 2025 and March 2026, a stretch in which the program was announced as ended and then restarted. Same agency, same week, same movie.
The Sandbox Has Left the Building
The same audit also examined FEMA GO, the system through which these applications are submitted and managed. At FEMA’s request, the OIG tested a sandbox that mirrors production, except that its data is synthetic and it lacks multifactor authentication. The auditors found it susceptible to manipulation and privilege escalation attacks. FEMA had implemented 3,488 of 4,163 required security settings, an 84 percent score, with no waivers or risk acceptances on file for the rest. Scans turned up two unique vulnerabilities in 50 occurrences, mostly missing updates.
FEMA’s August 19, 2026 response was to non-concur with all three recommendations and ask that they be closed. The argument is that the test environment was temporary, did not match the live system, relied on generic credentials the OIG agreed to, and no longer exists, so many findings are false positives or not applicable. FEMA also says it never saw the draft penetration test report before findings were finalized, and that it has addressed every validated finding through an approved plan of action and milestones.
The OIG answers that the two findings it cares about most, one involving personally identifiable information and one involving username exposure, apply to production as well, that FEMA never documented fixing them, and that FEMA’s own false-positive review still left vulnerabilities standing. The auditors add that they delivered the original report to FEMA’s chief information security officer in February 2025. The first meeting FEMA’s memo lists took place on June 11, 2026, sixteen months later. The OIG also says it accepted FEMA’s suggested rewording of the recommendations, which is why the text quoted in FEMA’s memo differs from the final report.
So the picture, as of this writing, runs as follows. Communities with repeatedly flooded buildings were selected for money, and then waited. The money has begun to move, in some amounts, from cycles FEMA has not specified, under a program whose newest edition requires a federal disaster declaration. The system that processes the applications was tested by the inspector general, found wanting, and defended by FEMA on the grounds that the room where the test took place has been demolished. The OIG will keep the recommendations open until FEMA submits a corrective action plan. The flood insurance policies, for their part, remain in force, and so does the weather.

