The Justice Department has a ubiquitous technical surveillance problem.
It does not have a department-wide definition for that problem. Until recently, it had no coordinated strategy for managing it. No individual or office had explicit responsibility for coordinating the response. And when auditors went looking for employee training specifically addressing the threat, they found none.
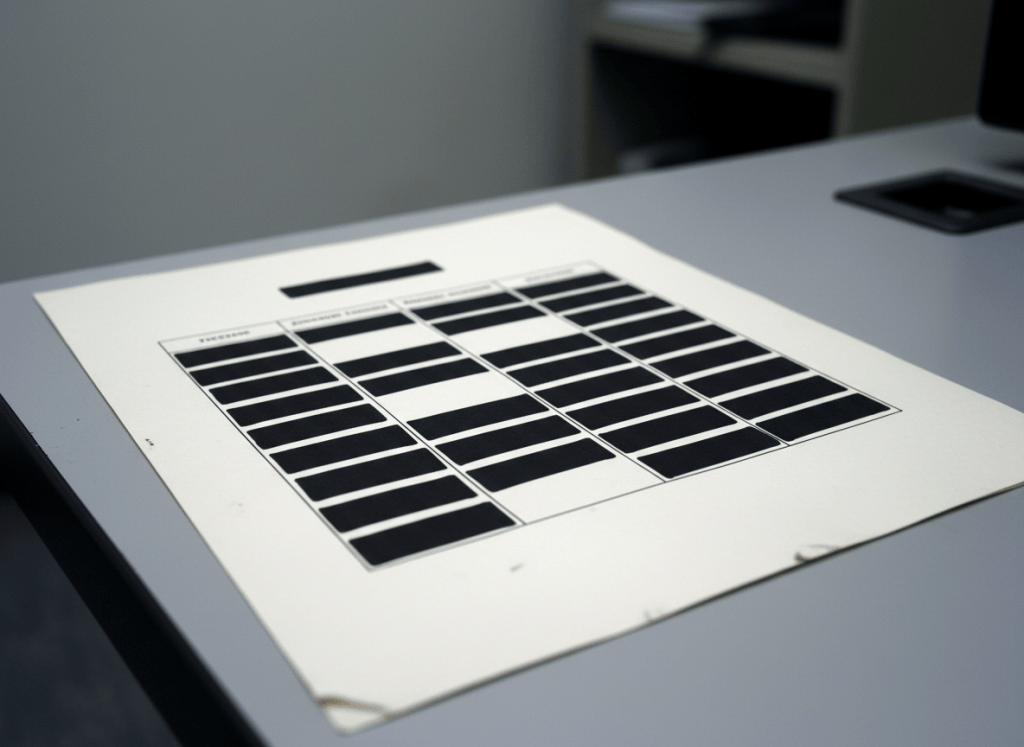
Then there is Table 2.
We would tell you what Table 2 says, but the Justice Department has blacked out essentially the entire thing.
That would ordinarily be little more than an irritating footnote in the world of federal records. In this particular report, however, the black boxes inadvertently provide a rather good demonstration of exactly what the Inspector General is warning about.
Bureaucracy Times received the report the decidedly unglamorous way investigative journalism occasionally happens. We entered an email address on a government website and subscribed to updates from the Department of Justice Office of Inspector General.
No classified records request. No FOIA lawsuit. No source slipping an envelope under the door.
We asked the government to send us its newsletter.
And the government sent us a report containing a table it apparently could not show us.
The digital trail everyone leaves behind
The September 2026 report, Audit of the Department of Justice’s Efforts to Mitigate the Effects of Ubiquitous Technical Surveillance, examines what DOJ calls UTS.
The concept is remarkably broad.
According to the OIG, ordinary use of technology and online services creates digital trails and discoverable connections. UTS involves capturing and analyzing that information to connect people with things, events or locations. The FBI divides the threat into five vectors: visual and physical surveillance, electronic signals, financial information, travel information and online activity.
A cellphone can reveal location information. Financial transactions contain identifiers. Hotel stays and airline reservations create records. Browsing and social-media activity generate advertising data.
Individually, those records may appear mundane.
Combined, they can tell a story.
Sometimes a deadly one.
The OIG’s previous 2025 audit of the FBI documented a drug-cartel investigation in which the cartel hired a hacker who exploited mobile phones and other electronic devices to obtain call and geolocation information. According to the Inspector General, that information was used to intimidate and, in some cases, kill potential sources or cooperating witnesses.
In another organized-crime investigation, call logs on an employee’s cellphone exposed communications with a known FBI-issued phone. The FBI lost the source.
These aren’t hypothetical privacy concerns dreamed up for the annual cybersecurity PowerPoint.
People can die.
Investigations can be compromised.
Sources can disappear.
And the OIG concluded that the problem extends well beyond the FBI.
DOJ had a threat without a strategy
Following its FBI audit, the Inspector General expanded its examination to the rest of the Justice Department.
What it found was not reassuring.
The auditors concluded that, outside the FBI, DOJ had not taken sufficient steps to manage the UTS threat. The deficiencies, according to the OIG, increased risks to Department employees, investigations, operations, sources and witnesses.
DOJ didn’t even have a common department-wide definition of ubiquitous technical surveillance.
The OIG found no individual or office explicitly responsible for coordinating DOJ’s response. There was no policy or guidance establishing how components should coordinate on UTS. And there was no single mechanism ensuring that information about emerging threats and mitigation practices moved throughout the Department.
Of 16 DOJ components and units interviewed outside the FBI, the auditors found that only the Drug Enforcement Administration’s Defensive Counterintelligence Unit had developed its own definition of UTS.
The DEA defined it as the widespread and continuous collection of data through technologies, often involving ordinary devices and activities, that can be connected back to an individual.
The FBI, meanwhile, was considerably further along.
Following the earlier OIG audit, the bureau designated UTS a “Tier 1 Enterprise Risk,” conducted an FBI-wide assessment, began developing a mitigation plan and training program, and continued working on an enterprise-wide UTS strategy.
The rest of DOJ was playing catch-up.
Forty-six courses. Zero dedicated to UTS.
Perhaps the cleanest measurement of that gap appears in the Department’s training records.
DOJ identified 46 training courses offered during fiscal years 2024 and 2025 that it believed might be related to ubiquitous technical surveillance.
The Inspector General checked.
None was UTS-specific.
Some courses touched subjects related to the threat, but according to the auditors, none actually described the UTS threat, explained how it might be exploited to DOJ’s advantage or taught personnel how to protect the Department from it.
Only seven of the 46 courses were mandatory.
Participation in the remaining voluntary courses among non-FBI DOJ personnel was less than 1 percent.
The mandatory offerings included general DOJ information-technology training, DEA’s Foreign Travel Briefing, ATF’s Counterintelligence Awareness and Security Training, and U.S. Marshals Service courses covering operations security.
The OIG concluded that DOJ had neither baseline UTS awareness training for its workforce nor specialized UTS training for employees working in particularly sensitive areas such as surveillance, source handling and counterintelligence.
There is a substantial difference between not recognizing a theoretical risk and failing to organize around a threat that has already materialized.
DOJ was dealing with the latter.
Immigration judges were already being targeted
During the current audit, DOJ told investigators about UTS-related incidents involving immigration judges overseeing cases handled by the Executive Office for Immigration Review.
Individuals had gathered publicly available but sensitive information about judges from disparate sources and published it in ways that could be used for intimidation or other purposes.
The response required coordination among DOJ security personnel, the U.S. Marshals Service and, sometimes, the FBI.
EOIR also employed a privacy and data-removal service to try to remove judges’ personal information from the internet.
That episode is particularly important because it demonstrates the defining characteristic of UTS.
The information does not necessarily have to begin as secret.
The danger comes from aggregation.
Take pieces of information that are individually public or innocuous, connect them, and something considerably more sensitive can emerge.
Which brings us back to Table 2.
About that table
On page three of the publicly released report sits a table.
Its title is redacted.
Its column headings are redacted.
Its row labels are redacted.
Its substantive entries are redacted.
Even the source printed beneath the table is redacted.
What remains visible is essentially its skeleton: four principal rows, two columns and a collection of bullet points hidden beneath black rectangles.
The OIG explains on the cover of the report that the complete version contains information the Justice Management Division considered law-enforcement sensitive and that those portions were removed to produce the public version.
There is nothing inherently scandalous about that.
Law-enforcement agencies possess information that shouldn’t be publicly released, and Inspector General reports routinely undergo redaction for legitimate reasons.
But the placement of this particular table was irresistible.
Immediately before Table 2, the OIG explains that it interviewed personnel from 12 non-law-enforcement components and subcomponents and four law-enforcement components, encompassing another 32 subcomponents. The auditors found a general lack of awareness and understanding of UTS across DOJ, although law-enforcement components were generally more aware of the threat than their non-law-enforcement counterparts.
Then comes the blacked-out table.
Immediately afterward, the report concludes that DOJ had taken no enterprise-level action to coordinate its components or actively manage department-wide vulnerabilities.
Naturally, we wanted to know what was underneath all that black ink.
So we tried to reconstruct it.
We failed
There are important distinctions here.
Bureaucracy Times did not attempt to remove the PDF’s redactions, exploit hidden document layers, recover deleted text or otherwise circumvent the government’s decision to withhold the material.
Instead, we tried something considerably less exciting.
We searched publicly available government records.
The theory was simple and, appropriately enough, almost identical to the threat described in the report itself: perhaps information appearing separately in other public DOJ, FBI, DEA or OIG records could be combined to independently establish what Table 2 contained.
We got surprisingly far.
The public report identifies the organizations auditors interviewed, including ATF, the Bureau of Prisons, DEA, U.S. Marshals Service, National Security Division, Criminal Division, Executive Office for United States Attorneys, Organized Crime Drug Enforcement Task Forces, Civil Division and EOIR, among others. The FBI was excluded from this particular audit because the OIG had already examined it separately.
We could establish that DEA’s Defensive Counterintelligence Unit had developed a UTS definition.
We could establish that EOIR had experienced the immigration-judge incidents.
We could establish that the Marshals Service participated in responses to those incidents.
We could establish that DEA, ATF and USMS offered training touching areas relevant to UTS.
What we could not establish was which organizations corresponded to the four visible rows of Table 2 or precisely what its individual bullet points said.
There were plausible candidates.
Plausible isn’t proof.
So we stopped.
The black boxes remain black.
Which rather proves the point
There is something wonderfully circular about the exercise.
DOJ’s Inspector General published a report explaining that seemingly ordinary pieces of information can be collected from disparate sources, connected together and used to reveal relationships that aren’t obvious when each piece is viewed independently.
DOJ then redacted information from that report because it was considered law-enforcement sensitive.
We received the redacted report because we had subscribed to a public government email list.
Then we attempted to combine other publicly available government records to determine whether the missing information could independently be reconstructed.
And we discovered that the public record gets you surprisingly far.
Just not far enough to responsibly fill in Table 2.
That may be the most appropriate ending imaginable for an Inspector General report about how much information can be reconstructed from seemingly ordinary pieces of data.
DOJ agrees changes are needed
The Justice Department isn’t contesting the Inspector General’s central findings.
The Justice Management Division’s Security and Emergency Planning Staff concurred with all three recommendations.
DOJ says it will develop a coordinated UTS strategy and governance framework, establish a structured process for identifying and monitoring risks, maintain a UTS risk portfolio and implement tiered training.
The Inspector General lists the recommendations as “resolved.”
That does not mean they’re finished.
The first recommendation will remain open until the OIG receives evidence that DOJ has actually established the coordinated strategy and assigned responsibility for managing its UTS risk portfolio. The second requires evidence that risks have been identified and mitigation plans developed.
The third will not close until DOJ demonstrates that it has created and implemented mandatory basic UTS awareness training across the Department, along with advanced training for employees occupying higher-risk positions.
That gives the Inspector General something concrete to measure later.
It gives us something to watch, too.
And if the Department eventually publishes a follow-up explaining how everything turned out, Bureaucracy Times is already subscribed to the newsletter.
We’ll check Table 2 first.


